
Information Security is at the heart of everything we do at Xtrm.

How to report a potential security issue?
If you believe you have found a security issue that pertains to Xtrm Technologies, we ask that you report it to us confidentially by emailing [email protected].
- Provide as much information on reproducing the issue as possible.
- The Xtrm security team will confirm receipt of your security concern in a timely manner.
- Please provide reasonable time for the Xtrm team to evaluate your report.
- Xtrm follows responsible disclosure and will credit researchers when a security issue has been identified and mitigated.
Where is customer data hosted?
Xtrm is a SaaS platform that is 100% cloud-based in Hyve cloud services. We do not operate our own physical servers, routers, load balancers, or DNS servers. All of our servers are within our own virtual private cloud (VPC) with network access control lists (ACLs) that prevent unauthorized requests from reaching our internal network. Role-based access control (RBAC) is used to ensure only employees that need access to customer data have access.
Hosting Facilities
Xtrm products run on world class infrastructure hosted at Hyve data centers running on cloud technology. Hyve data centers provide physical security 24/7, state of the art fire suppression, redundant utilities and biometric devices to ensure that our customers’ data is safe and secure. Hyve continually reviews and refines their procedures to comply with the latest security standards.
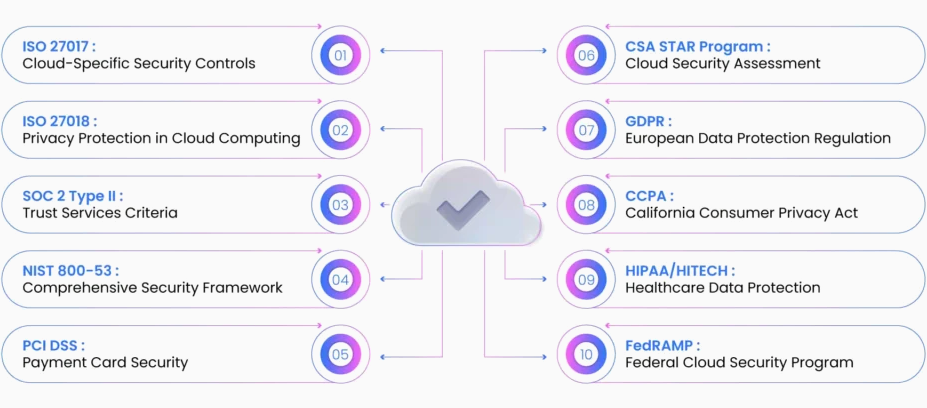
SOC 2 Type 2
Xtrm has a report on Controls at a Service Organization Relevant to Security available for review. To request the report, please contact [email protected].
This report is intended to meet the needs of a broad range of users that need detailed information and assurance about the controls at a service organization relevant to security of the systems the service organization uses to process users’ data and the confidentiality and privacy of the information processed by these systems. These reports can play an important role in:
- Oversight of the organization
- Vendor management programs
- Internal corporate governance and risk management processes
- Regulatory oversight
There are two types of reports: A type 2 report on management’s description of a service organization’s system and the suitability of the design and operating effectiveness of controls; and a type 1 report on management’s description of a service organization's system and the suitability of the design of controls. Use of this report is restricted.
GDPR and CCPA
Xtrm is headquartered in the U.S. and all personal data is processed in the United States. Xtrm continues to comply with the EU/Swiss-U.S. Privacy Shield Framework as set forth by the U.S. Department of Commerce regarding the collection, use, and retention of personal information from European Union member countries/Switzerland.
Xtrm is CCPA compliant. Please see our privacy policy for more information on how we process personal data.
Network Security
We protect communications between you and our systems. We take multiple steps to prevent eavesdropping between you and our systems, as well as within our infrastructure. For example, all network traffic runs over HTTPS (TLS), internal assets are isolated using strict filtering policies allowing only communication that is required and by default all access is denied and only explicitly allowed.
Security Operations
If we see something, we’ll react and remedy the issue. We’re not resting on our laurels. We’re looking for breaches and system interruptions all the time. We’ve invested in ensuring we can detect and respond to security events and incidents that impact our infrastructure. Security Operations at Xtrm is responsible for ensuring that:
- We respond to all Infosec and US-CERT alerts in an expedient fashion.
- Incidents are responded to and communicated to all appropriate parties.
- Corrective actions are executed.
- Root cause analysis is performed.
- Lessons learned are fed back to the appropriate internal teams.
System Security
We’re always updating our systems to protect your data. Our virtual systems are replaced on a regular basis with new, patched systems. System configuration and consistency is maintained using a combination of configuration management, up-to-date images and continuous deployment. Through continuous deployment, existing systems are decommissioned and replaced by up-to-date images at regular intervals.
Restricted Access
Only people who need access, get access. Production system access is limited to key members of the Xtrm Operations team and passwords are expressly forbidden. At a minimum, authentication requires two factors including asymmetric RSA public/private keys and a certificate based multifactored VPN connection.
Third Party Assessments
Don’t just take our word that our systems are secure. Even though Xtrm services and processes are designed with security in mind, regular vulnerability tests are run to identify and remediate potential weaknesses. Periodic penetration and web application security assessments are conducted under the guise of expert third party vendors to ensure our applications and services are continually scrutinized for potential risk. In addition these tests can include static code analysis, white box and black box testing for vulnerabilities.
Logging
We’re watching to find misuse or occasional problems. Logging is used extensively for application troubleshooting and investigating issues. Logs are streamed in realtime and over secure channels to a centralized logging service. This also allows our operations and development teams to view logs without the need to access the production systems. We collect everything from application logs to Hyve logs which form a complete audit trail of user and employee activity.
Application Level Security
We prevent single points of failure. Even if one system goes down or is breached, the rest of our services stay up and secure. All services are logically segmented following best practices, such as running applications services on dedicated instances. All login pages are secured via TLS over external and internal networks, and only certificates signed by well known Certificate Authorities (CAs) are allowed. All business-related communications, such as email and CRM, are encrypted while in transit as well as at rest. Xtrm customer application passwords are hashed and salted at rest and even our own staff can’t retrieve them — if lost the password must be reset.
Encryption
The Xtrm Security Ratings utilizes TLS encryption for all data in transit. Data at rest is encrypted using SHA encryption with salt to encrypt your data on the server that hosts your Hyve DB instances.
Data Protection, Continuity and Retention
We backup and test our systems, just in case. Production data is mirrored to remote systems and automatically backed up on a regular basis. Production databases are replicated to avoid single points of failure. Recovery procedures are tested regularly by restoring from backup and simulating recovery of a production database. Backup retention varies by function and business impact.
Internal IT Security
We protect our own systems to protect your data. Xtrm offices are protected behind network firewalls by well-known security vendors and secured by keycard access. Collaborative tools like email, document shares and calendars require two factor authentication to mitigate phishing attacks. Critical infrastructure passwords are locked in a virtual vault using AES256 encryption and can only be accessed by a handful of individuals in the organization.
Xtrm BUG Bounty
Xtrm maintains a managed bug bounty program allowing security researchers from around the world to ethically and responsibly research and disclose security vulnerabilities to our security team. To report a bug, please email [email protected] for review.
Training and Awareness
Xtrm requires all employees and contractors to sign a confidentiality agreement prior to commencement of employment or the provision of services. Security awareness training is delivered to all employees and contractors and we continually publicize security alerts through our internal communication channels.
Questions?
If you have any questions about our security, feel free to reach out to our security team at [email protected].
Security Features Overview
Complex Password Access
All access is via complex minimum 8 character passwords with numbers and special characters required.
SHA Encryption with Salt
All passwords unencryptable.
Access Lockout
Repeated failed attempts to access system blocks users and is logged.
IP Based Access
Specific IP based security for controlled access.
Location Based Access
Location based restrictions
One Time Passwords (2 step authentication)
Device and IP based
Web Application Firewalls
Realtime DOS, SQL Injection and other attack protection
Real time KYC validation (Know your customer)
Instant checks on individual and company details during profile setup and payments
Real time AML validation (Anti money laundering)
Instant rule checks on individual and company payments activity.
Secure Encrypted Data
Sensitive data encrypted using state of the art encryption methods. Details on request.
Regular Independent Site Scans
Regular third party scans of servers using Veracode and Trustwave to ensure no vulnerabilities including static and dynamic scans.
Firewall Protection
Secure firewall protection.
Physically Secure Servers
All servers in carefully monitored restricted site with secure passkey access. More information on request.
Safety Policies
Documented security policies in place.
Compliance
AML and KYC Compliance
The Xtrm platform and policies ensure all movement of money is controlled by strictly adhering to all global anti money laundering (AML) and know your customer (KYC) regulations. By collecting all required PII and company data, plus using advanced real-time KYC checking and identity level payment and velocity restrictions we can ensure you and your business maintain compliance at all times.
SOC 1 and SOC 2 Compliance
Xtrm is both SOC 1 and SOC 2 compliant, providing a significant level of security and controls that ensure payments are handled in a safe, secure and compliant manner. Through the use of advanced server infrastructure and state of the art security methodology, combined with strongly implemented and independently audited process control, we are able to ensure payments are handled quickly and efficiently regardless of how many and how much volume to anywhere in the world.
Money Transmitter Compliance
Xtrm has deployed a fully MTL licenced infrastructure to comply will all US and Non-US payment regulations. This includes regulatory requirements to ensure all payments are moved between identified companies and individuals in a controlled and secure manner. This also provides data and payment restrictions based on real-time KYC identity tracking as well as assurances around funds managed and held by Xtrm.
More information
PCI Compliance
Xtrm is fully PCI compliant to ensure card processing is safe and securely managed. This also provides data and payment restrictions based on real-time KYC identity tracking as well as assurances around funds managed and held by Xtrm.
GDPR Compliance
Xtrm adheres to all the data protections requirement set forth in GDPR providing all data subjects control of their personal data as well as processing all data using highly secure protocols.